GitLab Project, Repository, User, and Security Settings Guide
Learn GitLab project, repository, user, and security settings including roles, SSH keys, API tokens, pipeline schedules, protected branches, approvals, SAML, IP allowlist, webhooks, and DevOps best practices.
Repository access, project settings, permissions, and security controlsContents
GitLab Project, Repository, User, and Security Settings Guide
Learn the important GitLab options every DevOps engineer and project maintainer should understand: users, groups, roles, SSH keys, API tokens, pipeline schedules, protected branches, merge request approvals, SAML, IP allowlist, deploy keys, deploy tokens, webhooks, and repository security controls.
Animated walkthrough: GitLab options at a glance
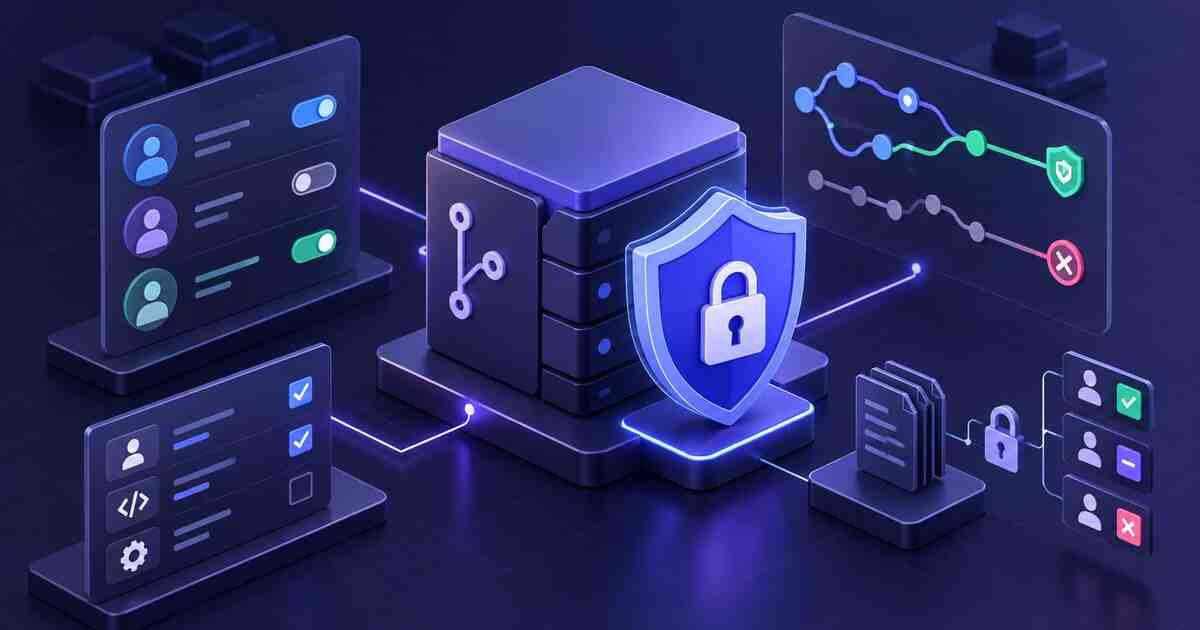
This video-style animation shows how the main GitLab administration and project settings work together. Use it as a quick visual map before going into each option below.
GitLab Settings Control Flow
Note: This is a lightweight animated explainer embedded in the article, so it loads quickly without needing an external video player.
Table of contents
Quick answer
Animated GitLab options walkthrough
Users, groups, and roles
SSH keys
API tokens, project tokens, deploy keys, and deploy tokens
Pipeline schedules
Branching strategy
Protected branches and tags
Merge request approvals
SAML, SSO, and IP allowlist
Webhooks and integrations
Project settings checklist
Related Melochip guides
Quick answer
Use roles carefully
Give users the minimum GitLab role they need. Do not make everyone Maintainer.
Protect production
Use protected branches, protected variables, protected environments, and approval rules for production workflows.
Separate access methods
Use SSH keys for Git access, access tokens for automation/API, and deploy keys/tokens for deployment use cases.
Automate safely
Use pipeline schedules, webhooks, and tokens, but rotate credentials and limit scopes.
1. Users, groups, and roles
GitLab access usually starts with users and groups. A user can be added directly to a project, or they can inherit access through a group. For real teams, group-based access is easier to manage than adding every user manually to every project.
Role
Typical use
Practical guidance
Guest
Very limited visibility
Use for users who only need basic visibility.
Reporter
Read/review access
Good for QA, auditors, support, or read-only project visibility.
Developer
Contribute code
Good default for engineers who need to push branches and create merge requests.
Maintainer
Manage project settings and releases
Use only for trusted leads who manage runners, protected branches, variables, and releases.
Owner
Group/project ownership
Use very carefully, usually for admins or group owners.
2. SSH keys configuration
SSH keys are commonly used for Git clone, pull, and push operations. A developer adds a public SSH key to their GitLab profile, then uses the matching private key from their local machine.
3. API tokens, project access tokens, deploy keys, and deploy tokens
Access option
Used for
Recommended usage
Personal access token
User-based API/Git access
Use only when automation must act as a specific user. Keep scopes limited.
Project access token
Project-scoped automation
Better for project automation than using a personal token.
Group access token
Group-scoped automation
Useful for automation across multiple projects in a group.
Deploy key
Repository access using SSH key
Good for server-side Git pull/clone use cases.
Deploy token
Repository/package/container registry access
Useful for read-only deployment or package download workflows.
4. Pipeline schedules
Pipeline schedules let you run pipelines automatically at a planned time. They are useful for nightly builds, weekly scans, scheduled reports, regular deployments, and cleanup jobs.
A branching strategy defines how code moves from development to release. Small teams may use a simple trunk-based model. Larger teams may use feature branches, release branches, and protected production branches.
feature/* branches for new changes.
Merge requests for review.
develop for integration/testing if your team uses a dev branch.
main for production-ready code.
Release tags for versioned production releases.
6. Protected branches and protected tags
Protected branches control who can push or merge into important branches. Protected tags control who can create release tags. These settings are important for production safety.
Setting
Why it matters
Example
Protected branch
Prevents direct risky changes
Protect main and release branches.
Allowed to merge
Controls who can merge approved code
Maintainers or selected groups.
Allowed to push
Controls direct pushes
Usually disabled for production branches.
Protected tag
Protects release version creation
Allow only release managers to create v* tags.
7. Merge request approvals and group approvals
Merge request approvals add review control before code is merged. Approval rules can require specific users, groups, or code owners to approve changes.
At least one maintainer approval for protected branches.
Code owner approval for sensitive folders.
Security team approval for security-sensitive changes.
DevOps approval for pipeline/deployment file changes.
QA approval before release branches are merged.
8. SAML, SSO, and IP allowlist
Enterprise GitLab setups often use SAML or SSO so users authenticate through the company identity provider. IP allowlist controls can restrict access to trusted networks depending on your GitLab edition and setup.
Feature
Purpose
Best practice
SAML/SSO
Centralized login through identity provider
Use for company-managed user authentication.
SCIM/user provisioning
Automated user lifecycle
Use where available for onboarding/offboarding.
IP allowlist
Restrict access to trusted IP ranges
Useful for sensitive groups/projects.
2FA
Extra authentication protection
Require for maintainers/admins where possible.
9. Webhooks and integrations
Webhooks notify external systems when GitLab events happen. Common events include push, merge request, pipeline, job, tag push, and release events.
Notify chat tools after pipeline failures.
Trigger external deployment tools.
Sync merge request events to project management tools.
Send release events to change-management systems.
Trigger security/compliance automation.
10. GitLab project settings checklist
Area
Recommended check
Users and groups
Use group-based access and least privilege.
Roles
Limit Maintainer/Owner access.
SSH keys
Remove old keys and require secure key handling.
Tokens
Use expiry, limited scopes, and rotation.
Variables
Use protected/masked/hidden variables for sensitive values.
Protected branches
Protect main , release branches, and production branches.
Merge approvals
Require reviews for important branches and sensitive files.
Pipeline schedules
Use schedules for recurring checks, not random manual work.
Webhooks
Secure webhook endpoints and secrets.
SAML/IP allowlist
Use enterprise controls where available.
Common mistakes
Giving Maintainer access to everyone.
Using personal access tokens for long-running automation.
Not setting token expiry dates.
Allowing direct pushes to production branches.
Keeping old SSH keys active after users leave or devices are replaced.
Running scheduled pipelines without clear ownership.
Creating webhooks without validating the receiving endpoint.
Using the same credentials for development and production.
Best practices
Use least privilege for users and automation.
Prefer group-based access management.
Protect production branches and release tags.
Use merge request approvals for sensitive changes.
Use project/group access tokens instead of personal tokens for automation where possible.
Rotate tokens and remove unused keys.
Use SAML/SSO and 2FA for enterprise access control where available.
Review project settings regularly.
Document who owns runners, schedules, variables, webhooks, and deployment credentials.
Screenshot checklist
You can add your own screenshots later from a safe test project:
Project members and roles screen with private details hidden.
SSH keys page with key values hidden.
Project access token creation page with token hidden.
Pipeline schedules list.
Protected branches settings.
Merge request approval rules.
Webhook settings with endpoint/token hidden.
SAML/SSO or group settings page with sensitive data hidden.
GitLab CI/CD Learning Path
GitLab CI/CD Variables and Secrets Explained
GitLab CI/CD Rules, Only, Except, and Workflow Explained
GitLab CI/CD Environments and Manual Deployments
GitLab CI/CD Troubleshooting Guide
GitLab CI/CD Security Scanning
Official references
GitLab project settings documentation
GitLab permissions documentation
GitLab SSH keys documentation
GitLab token security documentation
GitLab pipeline schedules documentation
Conclusion
GitLab is more than a repository and pipeline tool. For real DevOps teams, the important value comes from combining access control, branch protection, merge approvals, tokens, SSH keys, schedules, webhooks, SSO, IP allowlist, and CI/CD security settings.
Start with least-privilege roles, protect important branches, secure tokens and keys, control approvals, and review settings regularly. This gives your GitLab projects a safer and clearer administration model.







No comments yet. Start the discussion.