What is Kubernetes?
Kubernetes is an open-source container orchestration platform. It helps teams run containerized applications across multiple machines with scaling, self-healing, service discovery, rolling updates, storage, security controls and automation.
Animated mental model: from container to production
Table of contents
- Quick answer
- Why Kubernetes is needed
- How Kubernetes works
- Core Kubernetes components
- Important Kubernetes objects
- YAML example
- Basic kubectl commands
- Docker vs Kubernetes
- Real-world deployment flow
- Common mistakes
- Best practices
- Related guides
Quick answer
Kubernetes is not Docker
Docker builds and runs containers. Kubernetes manages many containers across many machines.
Pod is the smallest unit
Kubernetes does not directly run a Docker container as the top-level object. It runs containers inside Pods.
Deployment manages replicas
A Deployment keeps the desired number of Pods running and supports rolling updates and rollback.
Service gives stable access
Pods can be recreated with new IP addresses. Services give stable networking for accessing them.
Why Kubernetes is needed
Running one container on one machine is simple. Running hundreds of containers across many servers is not simple. In production, teams need a platform that can decide where containers run, restart failed workloads, scale applications, expose services, attach storage, apply configuration, and roll out changes safely.
That is where Kubernetes helps. Kubernetes lets you describe your desired state using YAML. For example, you can say: “Run three replicas of this application image, expose it internally through a Service, and update it using a rolling deployment.” Kubernetes then works continuously to keep the real cluster close to that desired state.
How Kubernetes works
A Kubernetes cluster has a control plane and worker nodes . The control plane makes decisions. Worker nodes run your applications.
- You write YAML or run a kubectl command.
- The request goes to the Kubernetes API server.
- Kubernetes stores the desired state.
- The scheduler decides which node should run the workload.
- The kubelet on that node starts the Pod using a container runtime.
- Kubernetes keeps watching the workload and repairs it if needed.
Core Kubernetes components
- Component — What it does — Beginner meaning
- API Server — Receives and validates Kubernetes requests — The front door of Kubernetes
- etcd — Stores cluster state — The database of the cluster
- Scheduler — Chooses where Pods should run — Decides the best worker node
- Controller Manager — Keeps desired state and actual state aligned — Fixes drift automatically
- kubelet — Runs on each worker node and manages Pods — The node agent
- kube-proxy — Handles Service networking rules — Helps route traffic
- Container runtime — Runs containers — Actually starts container processes
Important Kubernetes objects
- Object — Purpose — Example use
- Pod — Runs one or more containers — Nginx app Pod
- Deployment — Manages Pods and rolling updates — Run 3 replicas of an app
- ReplicaSet — Ensures a number of Pods exist — Created by Deployment
- Service — Stable network endpoint — Expose app inside cluster
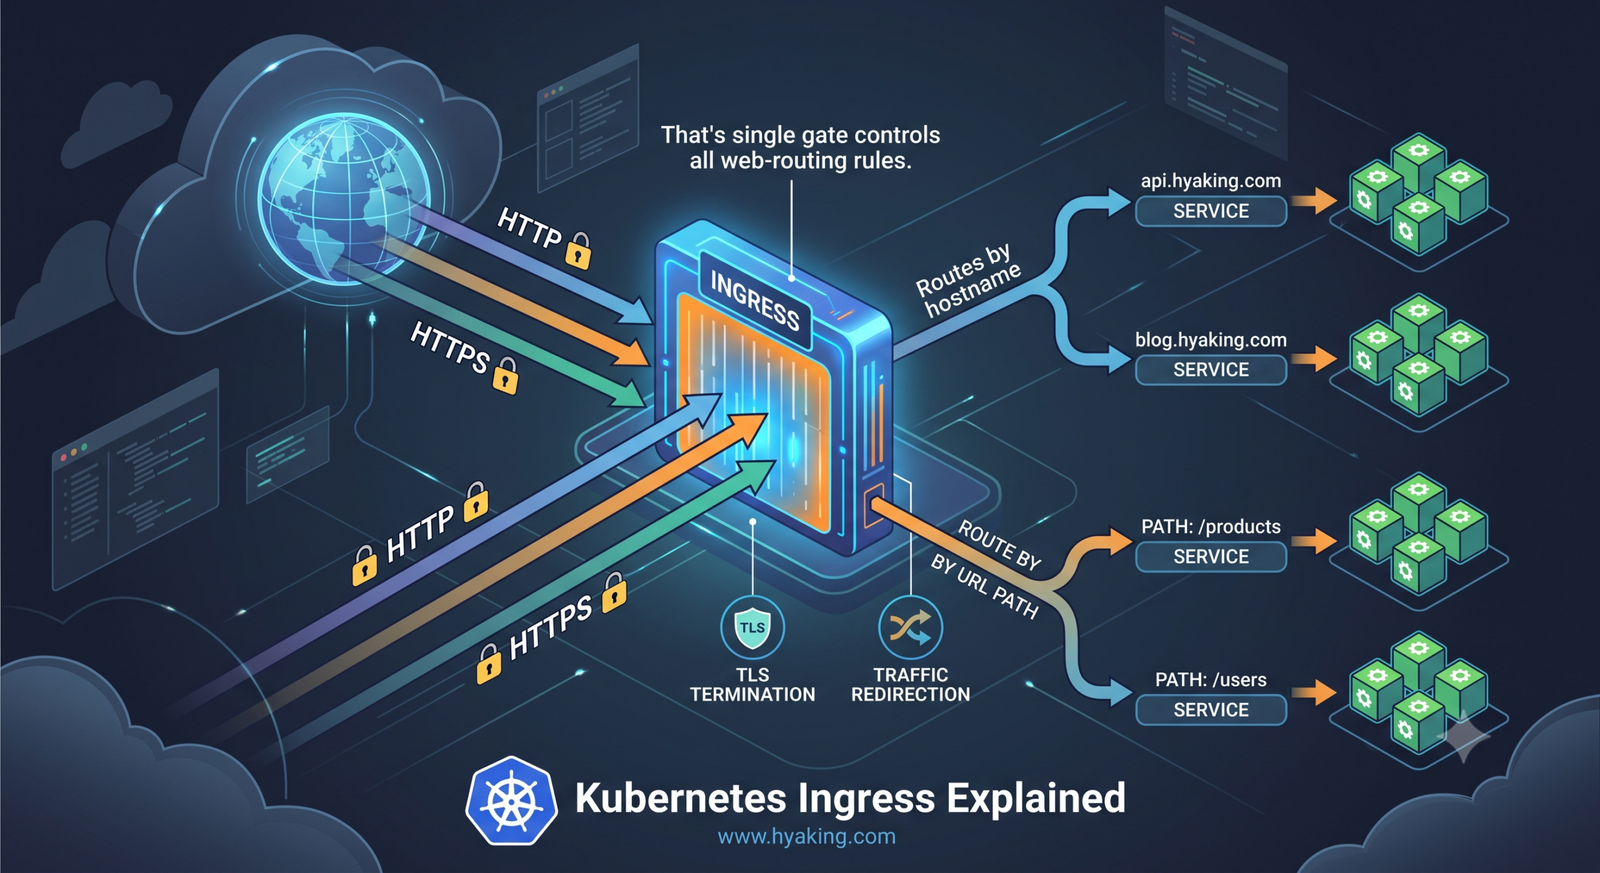
- Ingress — HTTP/HTTPS routing from outside — Route domain to service
- ConfigMap — Non-secret configuration — App config values
- Secret — Sensitive configuration — Passwords, tokens, keys
- PersistentVolumeClaim — Requests storage — Database data disk
- Namespace — Logical separation — dev, staging, production
Simple Kubernetes YAML example
This example creates a Deployment with two Nginx Pods and a Service to access them inside the cluster.
apiVersion: apps/v1 kind: Deployment metadata: name: nginx-deployment spec: replicas: 2 selector: matchLabels: app: nginx template: metadata: labels: app: nginx spec: containers: - name: nginx image: nginx:1.27 ports: - containerPort: 80 --- apiVersion: v1 kind: Service metadata: name: nginx-service spec: selector: app: nginx ports: - port: 80 targetPort: 80 type: ClusterIP
Apply the YAML
kubectl apply -f nginx.yaml kubectl get deployments kubectl get pods kubectl get svc
Basic kubectl commands
kubectl is the command-line tool used to talk to Kubernetes.
kubectl version --client kubectl cluster-info kubectl get nodes kubectl get pods kubectl get pods -A kubectl describe pod POD_NAME kubectl logs POD_NAME kubectl exec -it POD_NAME -- sh kubectl get events --sort-by=.metadata.creationTimestamp kubectl apply -f file.yaml kubectl delete -f file.yaml
Docker vs Kubernetes
- Area — Docker — Kubernetes
- Main job — Build and run containers — Orchestrate containers across a cluster
- Smallest unit — Container — Pod
- Scaling — Manual or Compose-based — Declarative replicas and autoscaling options
- Networking — Ports and Docker networks — Services, DNS, Ingress, NetworkPolicy
- Production management — Good for simple workloads — Designed for distributed production workloads
Real-world Kubernetes deployment flow
- Developer writes application code.
- Docker builds an application image.
- CI/CD pipeline tests the app and pushes the image to a registry.
- Kubernetes Deployment references that image tag.
- Pods start on worker nodes.
- Service exposes Pods inside the cluster.
- Ingress routes external domain traffic to the Service.
- Monitoring and logs help teams track health.
When should you use Kubernetes?
- You run multiple containers or microservices.
- You need rolling updates and rollback.
- You need self-healing workloads.
- You need service discovery and stable networking.
- You need scaling across multiple servers.
- You want platform-style deployment for teams.
When Kubernetes may be too much
- You have only one small app.
- You do not need scaling or orchestration.
- Your team is not ready for cluster operations.
- A simple VM, Docker Compose or managed platform is enough.
Common beginner mistakes
- Mistake — Why it hurts — Better approach
- Learning Kubernetes before Docker — Kubernetes concepts become confusing — Understand images, containers, volumes and networks first
- Using bare Pods in production — Pods are not self-managed enough — Use Deployments for applications
- Confusing Service and Deployment — Networking and scaling become unclear — Deployment runs Pods; Service exposes Pods
- Ignoring events — Troubleshooting takes longer — Use kubectl describe and kubectl get events
- Putting secrets in plain YAML — Credentials can leak — Use Kubernetes Secrets carefully and external secret managers for production
Best practices for beginners
- Learn Docker images and containers first.
- Start with Pods, then Deployments, then Services.
- Use namespaces for separation.
- Use labels consistently.
- Use kubectl describe , logs and events for debugging.
- Use Deployments instead of standalone Pods for applications.
- Use ConfigMaps for non-secret config and Secrets for sensitive config.
- Set resource requests and limits in real environments.
- Use official docs and test in a safe lab cluster.
Mini practice lab
After reading this article, try these simple tasks in a local or test cluster:
- Run kubectl get nodes .
- Create an Nginx Deployment.
- Scale it to three replicas.
- Create a Service for it.
- Check Pods, logs and events.
- Delete the Deployment and Service.
kubectl create deployment nginx-demo --image=nginx:1.27 kubectl scale deployment nginx-demo --replicas=3 kubectl expose deployment nginx-demo --port=80 --type=ClusterIP kubectl get pods kubectl get svc kubectl logs deployment/nginx-demo kubectl delete deployment nginx-demo kubectl delete svc nginx-demo
Related Melochip guides
- Kubernetes Learning Path
- Docker Learning Path
- Docker Images vs Containers Explained
- GitLab CI/CD Deploy to Kubernetes
- Terraform Kubernetes and Helm Deployments
- Kubernetes Cluster Setup Guide
Official references
- Kubernetes overview
- Kubernetes architecture
- Kubernetes Pods documentation
- kubectl reference
Conclusion
Kubernetes helps teams run containerized applications reliably at scale. It introduces new concepts such as Pods, Deployments, Services, Ingress, ConfigMaps, Secrets, Volumes and RBAC, but the core idea is simple: describe the desired state and let Kubernetes keep the cluster aligned with that state.
Start slowly. Understand Docker first, then learn Pods, Deployments, Services and kubectl commands. Once those are clear, Kubernetes becomes much easier to learn and use in real DevOps environments.
Join the discussion
0 CommentsAsk questions, add context, or share what worked.
More from Melochip Editorial
Learn what Playwright testing is, why modern QA teams use it, how testers can get started, and the major types...
7 min read · Sep 19, 2026
Learn how Kubernetes Deployments and ReplicaSets work with practical YAML, scaling, self-healing, rolling upda...
7 min read · Sep 17, 2026
Learn Kubernetes security best practices with RBAC, Secrets, ServiceAccounts, Pod securityContext, NetworkPoli...
6 min read · Sep 17, 2026Related articles
Learn how Kubernetes Deployments and ReplicaSets work with practical YAML, scaling, self-healing, rolling upda...
7 min read · Sep 17, 2026
Learn Kubernetes Ingress with controllers, IngressClass, host and path routing, TLS, DNS, annotations, redirec...
8 min read · Sep 17, 2026
Troubleshoot Kubernetes issues including Pending Pods, CrashLoopBackOff, ImagePullBackOff, service routing, in...
7 min read · Sep 17, 2026
Learn Kubernetes security best practices with RBAC, Secrets, ServiceAccounts, Pod securityContext, NetworkPoli...
6 min read · Sep 17, 2026Stay in the loop. Get new Melochip articles
Receive Melochip article updates when new articles are available. Explicit opt-in only.
No comments yet. Start the discussion.