Symmetric vs Asymmetric Encryption: AES, RSA, ECC and TLS
Compare symmetric and asymmetric cryptography, including AES, RSA, elliptic-curve methods, key establishment, digital signatures, TLS and secure key management.
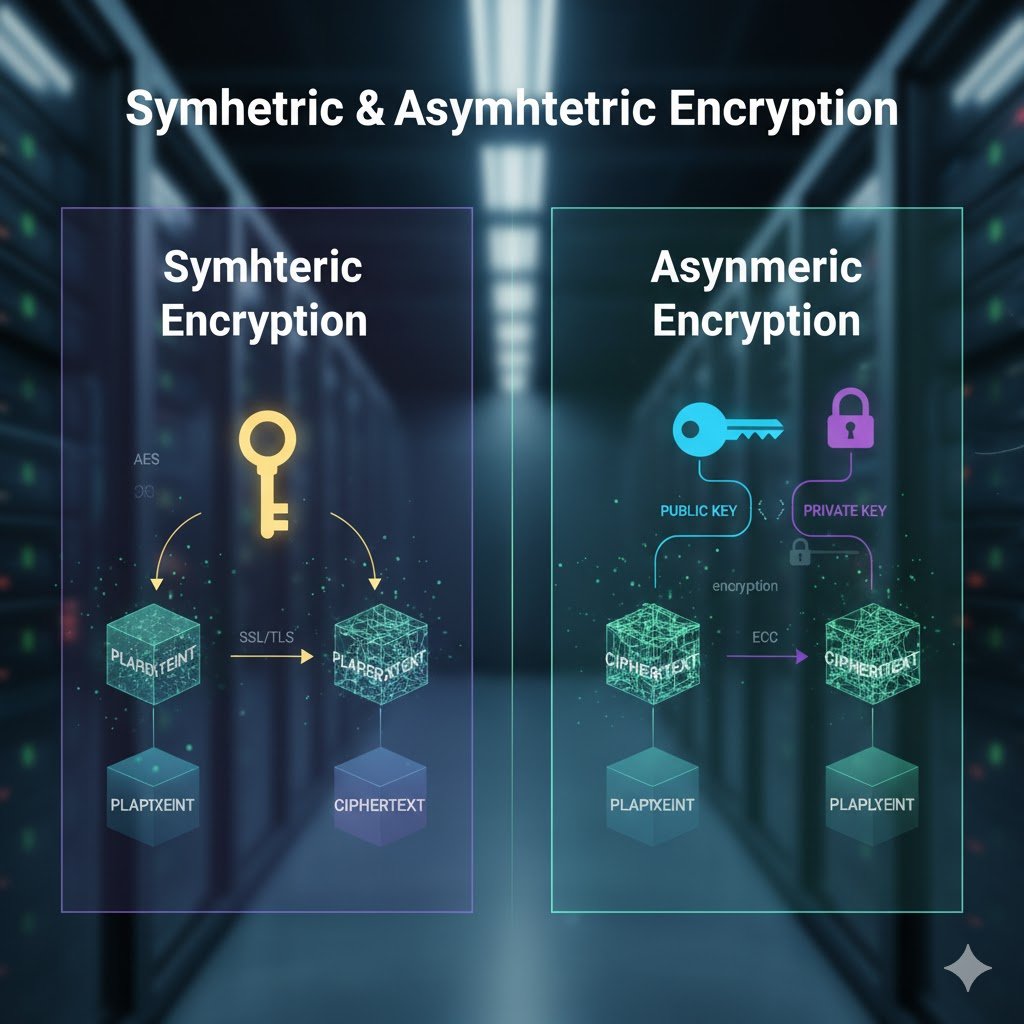
Symmetric and asymmetric encryption concepts represented by shared and public-private key securityContents
Last reviewed: September 2026
Encryption transforms readable plaintext into ciphertext so unauthorized parties cannot understand it. Symmetric and asymmetric cryptography solve different problems and are commonly combined in secure systems.
Symmetric encryption
Symmetric encryption uses the same secret key for encryption and decryption. It is efficient for large amounts of data, but every authorized party or service must obtain and protect the shared secret.
AES is the primary modern standardized symmetric block cipher.
Authenticated-encryption modes can provide confidentiality and detect modification.
Typical uses include disk, database, backup, VPN and application-data protection.
Security depends on the full construction: algorithm, mode, nonce handling, key generation, storage and rotation.
Asymmetric cryptography
Asymmetric cryptography uses a mathematically related public and private key pair. Public information can be distributed, while private key material must remain controlled. Different public-key schemes support encryption, key establishment or digital signatures; an algorithm should be used only for its intended purpose.
RSA is used in approved encryption and signature constructions, subject to current parameters and padding requirements.
Elliptic-curve schemes can provide key establishment and signatures with comparatively compact keys.
Public-key infrastructure binds identities to public keys through certificates and trust chains.
Asymmetric operations are more computationally expensive than symmetric bulk encryption.
Key differences
Area
Symmetric
Asymmetric
Keys
One shared secret
Public and private pair
Performance
Efficient for bulk data
Higher computational cost
Primary roles
Protect stored or transmitted data
Key establishment, identity and signatures
Main operational risk
Sharing, storing and rotating the secret
Protecting private material and validating public-key identity
Examples
AES
RSA and elliptic-curve schemes
Neither type is automatically more secure
Security cannot be decided only by choosing symmetric or asymmetric cryptography. It depends on approved algorithms and parameters, correct implementation, key protection, protocol design, random-number generation, certificate validation, update strategy and operational controls.
How hybrid encryption works
The client validates the service identity and certificate according to the protocol.
A key-establishment process derives shared session secrets.
Fast symmetric authenticated encryption protects application traffic.
Fresh session keys and protocol integrity controls limit exposure and detect tampering.
TLS 1.3 follows this hybrid model. Its handshake authenticates peers as configured and establishes keys, while authenticated symmetric encryption protects ongoing records.
Digital signatures are not encryption
A digital signature provides integrity, origin authentication and, depending on context and policy, evidence that a holder of the signing key approved specific data. Signing does not hide the signed content.
Operation
Primary goal
Encryption
Keep data confidential
Authentication tag
Detect modification and authenticate data under a shared secret
Digital signature
Verify integrity and public-key origin
Hash function
Create a fixed-length digest; not encryption
Key derivation
Derive one or more cryptographic keys from approved input material
AES, RSA and ECC in practice
AES commonly protects data at rest and bulk network traffic.
RSA may support signatures or approved encryption constructions, but raw textbook RSA is not safe.
Elliptic-curve Diffie-Hellman variants can establish shared secrets.
Elliptic-curve signature schemes authenticate software, documents or protocol participants.
Protocol libraries choose suites and combine primitives; applications should not invent these combinations.
Key management matters more than labels
Generate keys with an approved cryptographic random source.
Store keys in a suitable key-management service or hardware-backed boundary.
Separate key-administration responsibilities and restrict access.
Record ownership, purpose, allowed operations and rotation policy.
Back up or escrow keys only when the recovery design explicitly requires it.
Retire compromised or obsolete keys and re-encrypt data when necessary.
Audit key use without writing key material to logs.
Obsolete algorithms and patterns
DES, 3DES and RC4 are not appropriate choices for new general-purpose designs. Avoid unauthenticated or obsolete protocol configurations, hardcoded keys, reused nonces where uniqueness is required, raw public-key operations and custom cryptographic algorithms.
Post-quantum planning
Large organizations should maintain a cryptographic inventory and design for algorithm agility. Migration planning should follow current standards and vendor support rather than replacing classical algorithms with unreviewed experimental code.
Practical examples
Scenario
Typical combination
Full-disk encryption
Symmetric encryption with platform key protection
HTTPS
Certificates and key establishment plus symmetric authenticated encryption
SSH session
Public-key or other authentication plus encrypted session keys
Code signing
Asymmetric digital signature and certificate validation
Encrypted backup
Symmetric data encryption plus controlled key storage
Implementation checklist
Use a maintained protocol or cryptographic library.
Follow current standards for algorithms, modes, parameters and key sizes.
Use authenticated encryption where the design requires confidentiality and integrity.
Validate certificates, hostnames, purposes and trust chains correctly.
Handle nonces, initialization values and random input exactly as specified.
Test rotation, recovery, revocation and algorithm migration.
Obtain specialist review for high-risk or custom protocol designs.







No comments yet. Start the discussion.