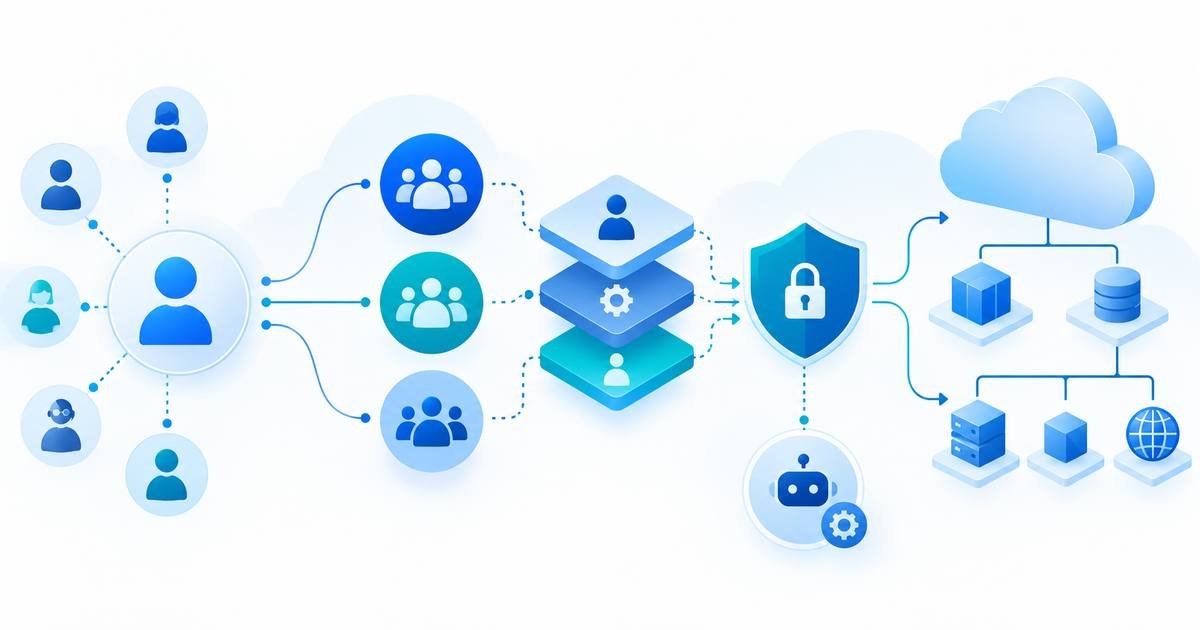
Abstract Azure identity and access control architecture with secure user groups, roles, and cloud resourcesContents
Azure Learning Path - Stage 1, Chapter 5. Azure security starts with identity. Microsoft Entra ID manages identities such as users, groups and applications, while Azure role-based access control determines what authenticated identities can do to Azure resources.
This chapter explains the difference between authentication and authorization, how users and groups are managed, how Azure RBAC scopes work, why least privilege matters, and how to assign access safely.
What You Will Learn
What Microsoft Entra ID is.
Users, groups, service principals and managed identities.
Authentication vs authorization.
Microsoft Entra roles vs Azure RBAC roles.
Azure RBAC scope and inheritance.
Built-in roles such as Reader, Contributor and Owner.
CLI examples and a least-privilege lab.
1. What Is Microsoft Entra ID?
Microsoft Entra ID is Microsoft's cloud identity and access platform. It stores and manages identities used to authenticate to Azure and many Microsoft and third-party services.
text
Identity
  |
Microsoft Entra ID
  |
Authentication
  |
Azure Resource Manager
  |
Azure RBAC authorization
  |
Azure Resource
A user existing in Microsoft Entra ID does not automatically mean that user can modify Azure resources. Resource authorization is controlled separately through Azure RBAC.
2. Common Identity Objects
Identity object
Purpose
User
Represents a person or user account.
Group
Groups identities so access can be assigned consistently.
Service principal
Application identity used by automation or applications.
Managed identity
Azure-managed identity that helps workloads authenticate without storing credentials in code.
3. Why Groups Are Better Than Repeated User Assignments
Suppose 25 engineers need Reader access to a production subscription. Assigning the role individually creates repetitive administration. A better pattern is to add users to a security group and assign the role to that group.
text
Users
  -> Azure-Prod-Readers group
  -> Reader role assignment
  -> Production subscription
4. Authentication vs Authorization
Concept
Question answered
Azure example
Authentication
Who are you?
Microsoft Entra ID validates the identity.
Authorization
What are you allowed to do?
Azure RBAC checks role assignments and scope.
5. Microsoft Entra Roles vs Azure RBAC Roles
Role system
Controls
Example
Microsoft Entra roles
Directory and identity administration
User Administrator
Azure RBAC roles
Azure resources
Virtual Machine Contributor
Do not assume that being a directory administrator automatically grants broad Azure subscription access.
6. Azure RBAC Model
text
Security principal + Role definition + Scope

Example:
CloudOps group + Reader + Subscription
Security principal: the identity receiving access, such as a user, group, service principal or managed identity.
Role definition: a collection of allowed management actions.
Scope: the Azure boundary where the permissions apply.
7. Azure RBAC Scopes
text
Management group
  -> Subscription
  -> Resource group
  -> Resource
A role assignment at a parent scope can be inherited by resources below it. Assigning access at the narrowest practical scope reduces unnecessary permissions.
8. Common Built-In Azure Roles
Role
Typical capability
Reader
View resources without changing them.
Contributor
Create and manage resources but generally cannot grant access.
Owner
Broad resource management plus ability to assign access.
User Access Administrator
Manage user access to Azure resources.
Azure also provides service-specific roles such as Storage Blob Data Reader and Virtual Machine Contributor. Prefer a specialized role when it meets the actual requirement.
9. Least Privilege
Least privilege means granting only the access required for the task, at the smallest useful scope, for only as long as necessary.
10. Azure CLI: Inspect Identity and Access
Terminal
$az account show --output table
az ad signed-in-user show --output table
az ad group list --output table
az role assignment list --output table
11. Create a Security Group Example
Terminal
$az ad group create \
--display-name Azure-Lab-Readers \
--mail-nickname azure-lab-readers
In enterprise environments, group naming, ownership and lifecycle should follow identity governance standards.
12. Assign Reader at Resource-Group Scope
Terminal
$GROUP_ID=$(az ad group show \
--group Azure-Lab-Readers \
--query id -o tsv)
az role assignment create \
--assignee-object-id "$GROUP_ID" \
--assignee-principal-type Group \
--role Reader \
--resource-group rg-azure-stage1-dev
az role assignment list \
--resource-group rg-azure-stage1-dev \
--output table
13. Managed Identities
Applications frequently need access to Azure services. Hard-coding usernames, passwords or client secrets in source code is risky. Managed identities allow supported Azure resources to obtain an Azure-managed identity and request tokens without storing a credential in application configuration.
text
App Service
  -> Managed Identity
  -> Key Vault Secrets User role
  -> Azure Key Vault
14. Security Best Practices
Require multifactor authentication according to organizational policy.
Use groups for repeatable access management.
Prefer least-privileged built-in roles.
Avoid permanent Owner assignments where they are unnecessary.
Use managed identities for Azure-hosted workloads where supported.
Review role assignments regularly.
Separate directory-administration privileges from Azure-resource privileges.
Do not share user accounts.
15. Common Mistakes
Confusing Microsoft Entra roles with Azure RBAC roles.
Giving Contributor when Reader is enough.
Assigning roles at subscription scope for a single-resource requirement.
Using individual user assignments everywhere instead of groups.
Putting application secrets in source control.
Assuming a newly created user automatically has subscription access.
16. Hands-On Lab
Create or identify a test resource group.
Create a test security group if permitted.
Add a test user only if your tenant policy allows it.
Assign the group Reader at the test resource-group scope.
Inspect the role assignment from the portal and CLI.
Compare inherited and direct role assignments.
Remove test role assignments and groups when finished if appropriate.
17. Interview Questions
What is Microsoft Entra ID?
What is the difference between authentication and authorization?
How are Microsoft Entra roles different from Azure RBAC roles?
What three components make up an Azure RBAC role assignment?
Why are groups useful for access management?
What is least privilege?
What is a managed identity and why is it useful?
What is the difference between Contributor and Owner?
Official References
Microsoft Learn: Entra user management
Microsoft Learn: Azure role-based access control
Microsoft Learn: Microsoft Entra role-based access control






No comments yet. Start the discussion.