Jenkins AI DevOpsDevSecOpsJenkinsModel Context Protocol

Article & Tutorial

How to Build a Secure Custom Jenkins MCP Server

Design a custom Jenkins MCP server with allowlisted tools, scoped API tokens, input validation, approval gates, audit logging, isolated build permissions, and safe client integration.

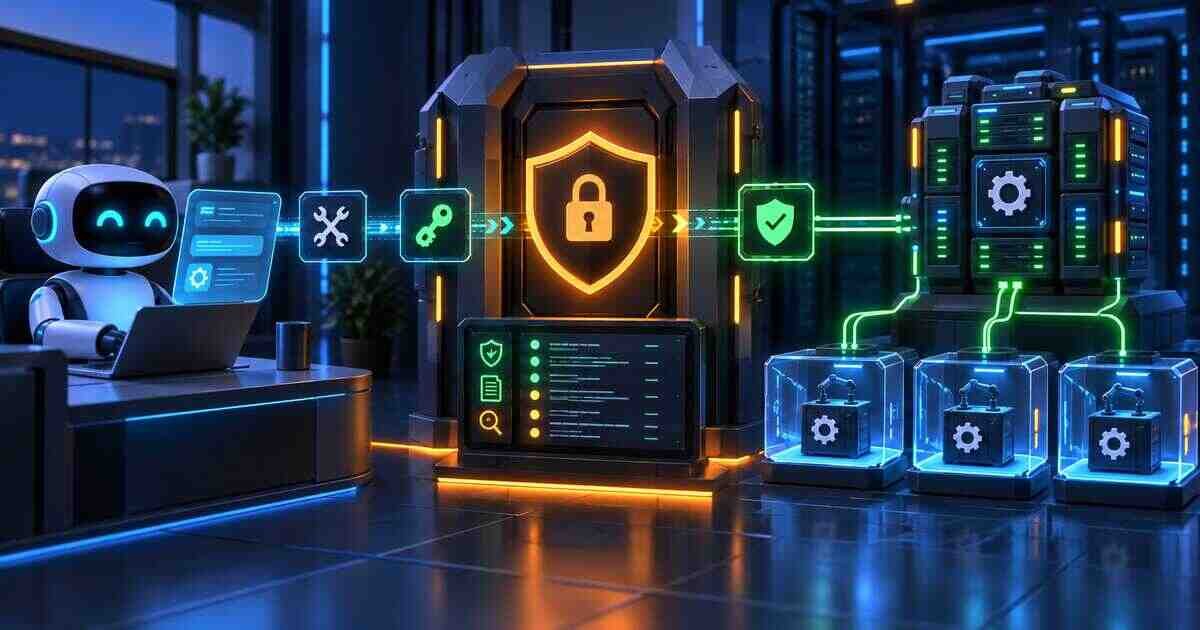
AI assistant connecting to Jenkins through a secure MCP gateway and isolated build agents
Contents

A custom Jenkins MCP server can expose a small set of approved Jenkins capabilities to an AI client without giving that client unrestricted controller access. The security boundary is the server: it must validate every request, enforce identity and policy, protect credentials, and record actions.

Recommended architecture

Place the MCP server between the AI client and Jenkins. The server translates typed tool requests into narrowly scoped Jenkins API calls. Keep Jenkins tokens only on the server, use a dedicated service identity, and restrict network access from the gateway to the controller.

Start with read-only tools

ToolSafe bounded result
list_jobsApproved job names and basic state
get_job_statusCurrent state for one allowlisted job
get_build_summaryNumber, result, duration, and timestamp
get_console_excerptRedacted bounded log segment
get_queue_statusApproved queued items without secrets

Add build-triggering tools only after read-only behavior is stable. Separate production and non-production permissions, require explicit parameters, and consider human approval for any action that changes state.

Jenkins identity and authorization

  • Create a dedicated service account instead of reusing an administrator.
  • Grant access only to approved folders, jobs, and API actions.
  • Use a managed secret store and rotate API tokens.
  • Restrict the service account from script console, credential administration, node management, and configuration changes.
  • Use network policy so the gateway cannot reach unrelated internal services.

Validate every tool request

Use strict schemas, reject unknown fields, normalize job identifiers, and compare them against an allowlist. Limit log size, time range, pagination, and concurrency. Never accept an arbitrary URL, Groovy script, shell command, file path, or raw Jenkins API route from the client.

Protect secrets in logs and responses

Jenkins masking is not a complete data-loss control. Redact credentials, tokens, headers, environment variables, signed URLs, and sensitive parameters again at the gateway. Return concise structured summaries instead of entire console logs by default.

Approval and audit

  1. Authenticate the MCP client and map it to an identity.
  2. Authorize the exact tool, job, and environment.
  3. Show the intended action and parameters before approval.
  4. Use an idempotency key for state-changing requests.
  5. Record requester, tool, target, result, timestamp, and correlation ID.
  6. Alert on repeated denials, unusual volume, or sensitive job access.

Testing before production

  • Schema validation and malformed input tests.
  • Authorization tests for every job and environment boundary.
  • Secret-redaction tests with synthetic credentials.
  • Rate-limit, timeout, and retry tests.
  • Jenkins outage and partial-response behavior.
  • Prompt-injection tests against console-log content.
  • Audit completeness and incident investigation exercises.

Deployment guidance

Run the gateway as an isolated service, terminate encrypted transport, patch dependencies, pin versions, monitor latency and error rates, and provide a rapid disable switch. Keep tool descriptions precise so the client understands boundaries without inferring unsupported powers.

Jenkins Remote Access API

Did this help?

Yes No

Join the discussion

0 Comments

Ask questions, add context, or share what worked.

Sign in to join the discussion

No comments yet. Start the discussion.

More from Melochip Editorial

Related articles

Stay in the loop. Get new Melochip articles

Receive Melochip article updates when new articles are available. Explicit opt-in only.

No pre-checked boxes. Unsubscribe support is part of the subscriber foundation.