GitLab GitLab CI/CDGitLab RunnersRunner Security

Article & Tutorial

GitLab Runner Security Best Practices: Protect CI/CD Jobs, Secrets, and Deployments

Learn GitLab Runner security best practices for protected runners, secrets, isolation, trusted deployments, executor choices, and CI/CD risk reduction.

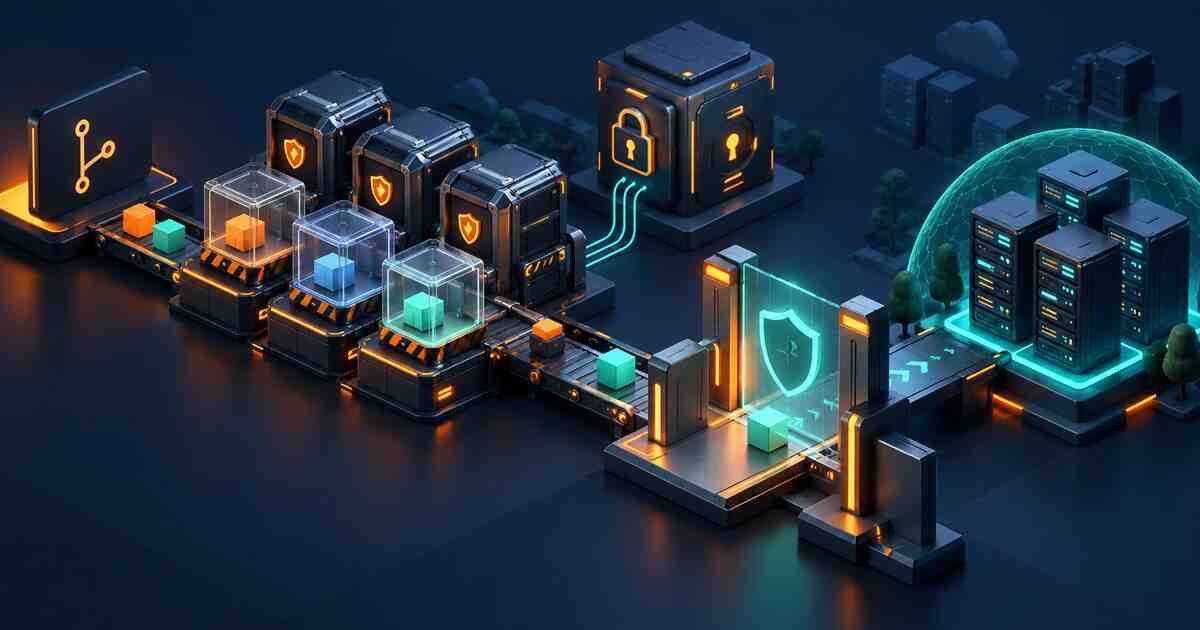
Hardened CI/CD runners with isolated jobs, protected secrets, and deployment gate
Contents

GitLab Runner Security Best Practices

Learn how to secure GitLab runners, protect CI/CD secrets, isolate jobs, control production deployments, and reduce risk from untrusted pipelines.

Quick answer

Protect sensitive jobs

Production deployment jobs should run only on trusted protected runners.

Limit secrets

Expose production variables only to protected branches and trusted jobs.

Separate workloads

Do not mix untrusted test jobs and production deployment jobs on the same runner.

Why runner security matters

A GitLab runner executes pipeline commands. That means it can access source code, environment variables, artifacts, container images, deployment credentials, and internal networks depending on your configuration.

Use runner isolation

  • Use separate runners for build, test, security scan, and production deployment workloads.
  • Use Docker or Kubernetes executors for better job isolation where suitable.
  • Avoid running untrusted code on privileged runners.
  • Do not let feature-branch jobs access production credentials.

Use protected runners

Protected runners help restrict sensitive jobs to protected branches or tags. This is useful for production deployment pipelines and release workflows.

deploy_production: stage: deploy tags: - production-runner script: - echo "Deploying safely" rules: - if: '$CI_COMMIT_BRANCH == "main"' when: manual - when: never

Protect variables and secrets

  • Use protected variables for production secrets.
  • Use masked variables where possible.
  • Use file variables for kubeconfig-style content.
  • Never echo secrets in logs.
  • Rotate tokens and credentials regularly.

Runner executor security notes

ExecutorSecurity note
ShellSimple but jobs run directly on the runner host. Use carefully.
DockerGood isolation for many projects, but privileged mode increases risk.
KubernetesGood for scalable isolated workloads, but needs cluster security controls.

Common mistakes

  • Using privileged Docker runners for every job.
  • Running external/untrusted merge request jobs with secrets.
  • Not patching runner hosts.
  • Using long-lived tokens without rotation.
  • Using the same runner for tests and production deployments.

Best practices checklist

  • Separate trusted and untrusted workloads.
  • Use protected runners for production jobs.
  • Use runner tags intentionally.
  • Keep runner software and host OS updated.
  • Restrict who can register and manage runners.
  • Monitor runner logs and resource usage.
  • Use least-privilege deployment credentials.
  • GitLab CI/CD Learning Path
  • GitLab CI/CD Security Scanning
  • GitLab CI/CD Best Practices

Official references

  • GitLab Runner security documentation
  • Configure GitLab runners

Did this help?

Yes No

Join the discussion

0 Comments

Ask questions, add context, or share what worked.

Sign in to join the discussion

No comments yet. Start the discussion.

More from Melochip Editorial

Related articles

Stay in the loop. Get new Melochip articles

Receive Melochip article updates when new articles are available. Explicit opt-in only.

No pre-checked boxes. Unsubscribe support is part of the subscriber foundation.