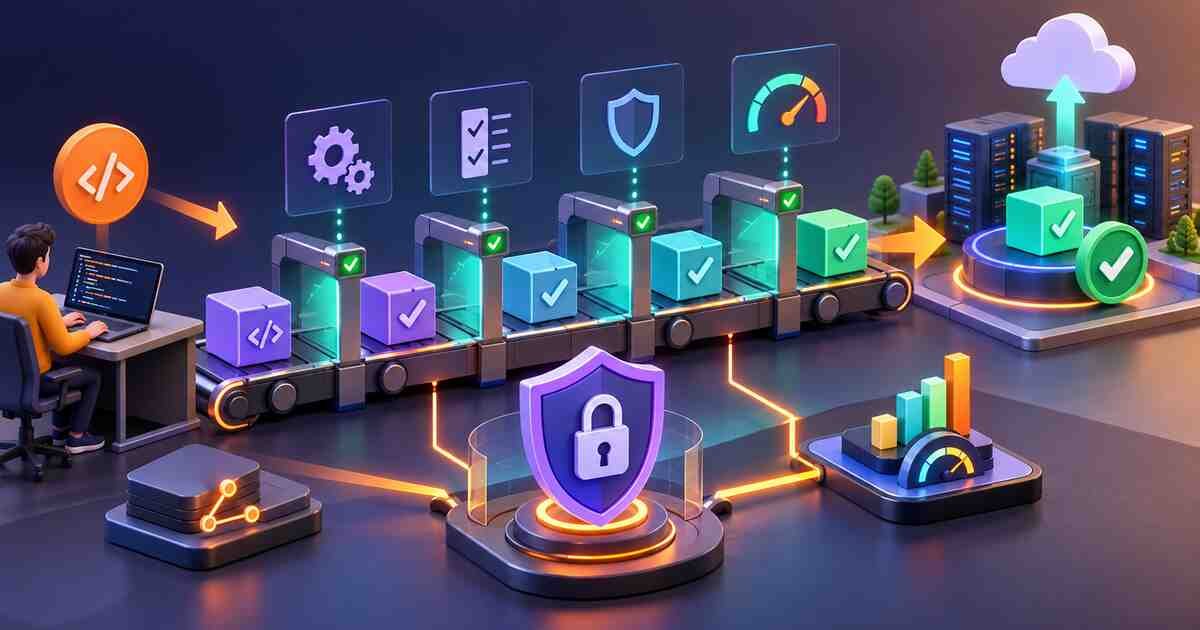
GitLab CI/CD Best Practices for DevOps Teams
Learn practical GitLab CI/CD best practices for building secure, fast, reliable, and maintainable pipelines. This guide covers pipeline structure, YAML standards, runners, variables, secrets, artifacts, cache, rules, security scanning, Docker images, Kubernetes deployments, approvals, monitoring, and team standards.
Table of contents
- Quick answer
- Pipeline structure
- YAML standards
- Rules and workflow
- Runner best practices
- Variables and secrets
- Artifacts and cache
- Security and DevSecOps
- Docker image best practices
- Deployment best practices
- Monitoring and troubleshooting
- Team checklist
- Related Melochip guides
Quick answer
Keep pipelines readable
Use clear stages, job names, comments, templates, and a predictable structure.
Fail fast
Run lint, syntax, unit tests, and small checks early so developers get feedback quickly.
Protect secrets
Use protected, masked, hidden, and file variables where appropriate. Never print secrets in logs.
Optimize carefully
Use cache, artifacts, needs , parallel jobs, and smaller Docker images to reduce pipeline time.
1. Use a clean pipeline structure
A good GitLab pipeline should be easy to read before it becomes advanced. Start with simple stages and grow carefully.
stages: - validate - test - security - build - deploy
A practical stage design:
- validate for linting, formatting, and YAML checks.
- test for unit tests and integration tests.
- security for SAST, dependency scanning, secret detection, and container scanning.
- build for packages, compiled output, or Docker images.
- deploy for development, staging, and production deployment.
2. Create YAML standards for the team
GitLab pipelines are defined in .gitlab-ci.yml . Without team standards, YAML files can become messy very quickly.
Recommended YAML standards
- Use clear job names such as run_unit_tests instead of job1 .
- Keep scripts short and move complex logic into version-controlled shell scripts.
- Use comments for non-obvious rules or deployment logic.
- Use includes/templates when multiple projects share the same pattern.
- Validate YAML using CI Lint before merging changes.
- Document required variables near the pipeline or in the project README.
run_unit_tests: stage: test image: node:20 script: - npm ci - npm test
3. Use rules and workflow intentionally
Do not run every job on every branch. Use rules and workflow to control when pipelines and jobs should run.
run_tests: stage: test script: - npm test rules: - if: '$CI_PIPELINE_SOURCE == "merge_request_event"' - if: '$CI_COMMIT_BRANCH == "main"'
Use rules for:
- Merge request pipelines.
- Main branch pipelines.
- Release branch pipelines.
- Scheduled pipelines.
- Manual production deployments.
- Skipping expensive jobs when unrelated files changed.
4. Runner best practices
GitLab Runner is the execution engine for CI/CD jobs. Poor runner design creates slow pipelines, stuck jobs, and security risk.
- Use runner tags intentionally.
- Separate trusted runners from untrusted workloads.
- Do not run production deployments on random shared runners.
- Keep runners updated.
- Monitor runner CPU, memory, disk, and queue time.
- Use Docker executor or Kubernetes executor where it fits your team.
- Limit who can register and manage runners.
5. Protect variables and secrets
Variables are powerful, but they are also one of the most common places where teams make mistakes.
| Secret type | Recommended handling |
|---|---|
| API tokens | Use limited scopes and expiry dates. |
| Production credentials | Use protected variables and protected branches. |
| Kubeconfig files | Use file variables where possible or write carefully during the job. |
| Registry passwords | Use CI/CD variables or built-in registry variables. |
| Cloud credentials | Use least privilege and rotate regularly. |
6. Use artifacts and cache correctly
Artifacts and cache are not the same.
| Feature | Use for | Example |
|---|---|---|
| Artifacts | Required output passed to later jobs | dist/ , reports, packages, test results |
| Cache | Speeding up dependency downloads | .npm/ , Maven cache, Gradle cache, pip cache |
build_app: stage: build script: - npm ci - npm run build artifacts: paths: - dist/ expire_in: 1 week
7. Add security scanning early
Security scanning should not be an afterthought. Add basic checks early, then improve over time.
- Use SAST for source-code scanning.
- Use dependency scanning for third-party packages.
- Use secret detection to catch accidental credential commits.
- Use container scanning when Docker images are built.
- Review findings and prioritize high/critical issues.
include: - template: Jobs/SAST.gitlab-ci.yml - template: Jobs/Secret-Detection.gitlab-ci.yml
8. Optimize Docker image usage
Docker images can make pipelines reliable, but large images and repeated installs can slow everything down.
Docker best practices
- Use the smallest practical base image.
- Use a job-specific image instead of one huge image for every job.
- Use custom CI images when repeated setup takes too long.
- Use .dockerignore to reduce build context size.
- Use commit SHA or version tags instead of relying only on latest .
- Scan container images before deployment.
9. Keep deployments controlled
Deployment jobs should be more controlled than normal test jobs. Production deployment needs extra protection.
deploy_production: stage: deploy script: - echo "Deploying to production" environment: name: production rules: - if: '$CI_COMMIT_BRANCH == "main"' when: manual - when: never
Deployment best practices
- Use environments for development, staging, and production.
- Use manual jobs for production.
- Use protected branches and protected variables.
- Limit who can deploy to production.
- Verify rollout after deployment.
- Document rollback steps and test them.
10. Monitor pipeline health
Best practices do not stop after writing YAML. Teams should monitor pipeline duration, failure rate, slow jobs, runner capacity, artifact storage, and recurring problems.
- Track slow jobs and long stages.
- Identify flaky tests.
- Review pipeline duration over time.
- Monitor runner resource usage.
- Reduce unnecessary scheduled jobs.
- Document recurring failures and fixes.
GitLab CI/CD best practices checklist
| Area | Best practice |
|---|---|
| Pipeline structure | Use clear stages and readable job names. |
| YAML | Validate with CI Lint and keep scripts simple. |
| Rules | Run jobs only when needed. |
| Runners | Use trusted runners for sensitive jobs. |
| Secrets | Use protected/masked/hidden/file variables where appropriate. |
| Artifacts | Use artifacts for required job output. |
| Cache | Use cache for dependency speed only. |
| Security | Add SAST, secret detection, dependency scanning, and container scanning where useful. |
| Docker | Use smaller images and safe tags. |
| Deployment | Use manual protected production deployments. |
| Monitoring | Track duration, failures, runners, and storage. |
Common mistakes
- Making every job run on every branch.
- Using cache as required build output.
- Using one huge Docker image for all jobs.
- Giving too many users Maintainer access.
- Putting secrets in YAML files or job logs.
- Deploying to production automatically without approvals.
- Ignoring slow pipelines until developers stop trusting CI/CD.
- Not documenting pipeline variables and ownership.
Screenshot checklist
You can add safe screenshots later from a sample project:
- Pipeline graph showing validate, test, security, build, deploy.
- CI/CD variables page with values hidden.
- Runner settings with tags visible but tokens hidden.
- Manual production deployment button.
- Security scanning jobs in pipeline.
- Pipeline duration or analytics view.
- GitLab CI/CD Learning Path
- GitLab CI/CD YAML Syntax Explained
- GitLab Artifacts vs Cache Explained
- GitLab CI/CD Security Scanning
- GitLab CI/CD Troubleshooting Guide
- GitLab Project, Repository, User, and Security Settings Guide
Official references
- GitLab pipeline efficiency documentation
- GitLab CI/CD YAML syntax reference
- GitLab Runner documentation
- GitLab CI/CD variables documentation
Conclusion
GitLab CI/CD best practices are about balance. Pipelines should be simple enough for developers to understand, secure enough for production, fast enough for daily work, and reliable enough for releases.
Start with clean stages, clear YAML, protected secrets, trusted runners, artifacts/cache discipline, security scanning, and controlled deployments. Then monitor pipeline health and improve step by step.
Join the discussion
0 CommentsAsk questions, add context, or share what worked.
More from Melochip Editorial
Learn what Playwright testing is, why modern QA teams use it, how testers can get started, and the major types...
7 min read · Sep 19, 2026
Learn how Kubernetes Deployments and ReplicaSets work with practical YAML, scaling, self-healing, rolling upda...
7 min read · Sep 17, 2026
Learn Kubernetes security best practices with RBAC, Secrets, ServiceAccounts, Pod securityContext, NetworkPoli...
6 min read · Sep 17, 2026Related articles
Learn Kubernetes security best practices with RBAC, Secrets, ServiceAccounts, Pod securityContext, NetworkPoli...
6 min read · Sep 17, 2026
Learn Kubernetes ConfigMaps and Secrets with YAML, environment variables, file mounts, update behavior, immuta...
8 min read · Sep 17, 2026
Learn Linux from the ground up with simple explanations of the kernel, distributions, filesystem, commands, pe...
4 min read · Updated Oct 1, 2026
Prepare for Docker interviews with practical questions and real-time scenarios covering images, containers, Do...
2 min read · Sep 17, 2026Stay in the loop. Get new Melochip articles
Receive Melochip article updates when new articles are available. Explicit opt-in only.
No comments yet. Start the discussion.